

Endpoint Management and Security Start with Autonomous IT
As environments scale and tools sprawl, visibility gaps keep widening — and it's no longer just a security team problem. Nearly half of compromised systems holding corporate credentials are unmanaged (Verizon 2025 DBIR), and attackers now exploit vulnerabilities in a mean time of just 7 days. If your team is still working from spreadsheets, stale scans, and a patchwork of point tools, this is worth 15 minutes of research before it becomes an incident. Learn why almost half of compromised systems with corporate credentials turn out to be unmanaged, how tool sprawl quietly fragments visibility across IT and security teams, and why "patch complete" doesn't always mean "patch verified." See how real-time endpoint intelligence is replacing periodic, stale vulnerability scans, and how enterprises like Honeywell and McDonald's are closing these gaps with autonomous IT at scale.
Ultimate Guide for IT Security Leaders: Closing the Exposure-to-Remediation Loop
Vulnerability discovery has never been faster — but remediation is still stuck behind slow handoffs between teams. This guide introduces a closed-loop framework — Identify, Prioritize, Validate, Remediate — built on continuous, real-time telemetry rather than point-in-time scans, so exposure management and remediation finally operate as one connected motion. Download the guide to see the four-step framework for closing the loop from detection to verified remediation in a single platform, how continuous validation cuts time spent chasing false positives and stale risk data, and real customer impact from AstraZeneca and JLL, who cut remediation time and reporting friction using this approach.
G2 report: AI That Acts: What IT and security teams are buying, and what it takes to trust it
A new G2 research report commissioned by Tanium, based on interviews with 118 IT and security leaders, reveals that AI buying is shifting from advisory tools to autonomous action. While 43% of leaders now want AI capable of low-risk execution with human oversight, governance remains front and center — 99% cite compliance or security constraints, and 67% require human approval before AI acts. With 84% naming AI or automation a top priority for the next 6–18 months, the report argues that vendors offering proven, auditable, governed autonomy today are best placed to lead as the next wave of AI matures.
Binding Authentication Back to the Original IDV Event Is Where Most Stacks Fall Short
This guide gives IAM practitioners a fast, engineering‑ready path to modernize, without breaking authentication flows or adding migration risk.
New Account Fraud Is Rising. Your Onboarding Flow Is Where It Starts.
This guide gives IAM practitioners a fast, engineering‑ready path to modernize, without breaking authentication flows or adding migration risk.
Ten Capability Gaps That Legacy CIAM Cannot Close at Runtime
This guide gives IAM practitioners a fast, engineering‑ready path to modernize, without breaking authentication flows or adding migration risk.
Your CIAM Platform Is Either Building Trust or Eroding It. There Is No Middle Ground.
This guide gives IAM practitioners a fast, engineering‑ready path to modernize, without breaking authentication flows or adding migration risk.
Reduce IAM Complexity with a Cloud‑Ready Identity Model
This guide gives IAM practitioners a fast, engineering‑ready path to modernize, without breaking authentication flows or adding migration risk.
Upgrade Your IAM Seamlessly for Efficiency and Resilience
This guide gives business leaders a clear, practical roadmap for shifting from self‑managed identity infrastructure to Ping’s cloud.
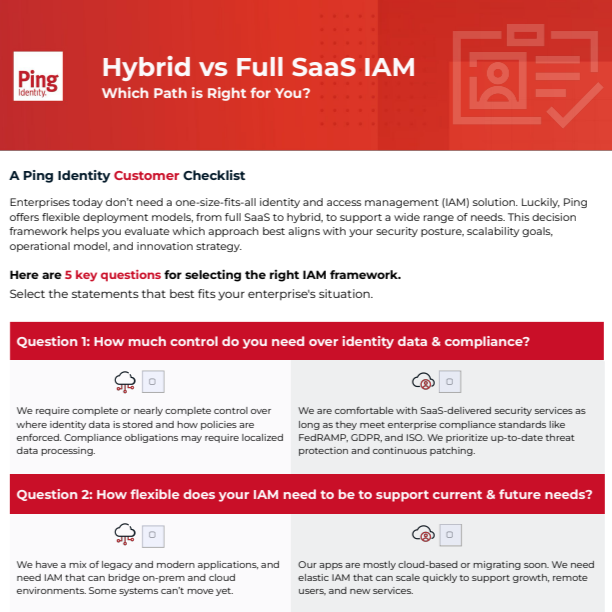
Validate Your IAM Architecture for Cloud-Ready Scale
This checklist helps IAM practitioners validate whether hybrid or full‑SaaS IAM aligns with their technical landscape.
Choose The IAM Strategy That Protects Revenue and Reduces Risk
This executive checklist helps you quickly determine whether a hybrid or full‑SaaS IAM model best supports your business outcomes.
Navigating Content Abundance | The Future of Marketing in the age of GenAI
Discover how to use AI’s potential to elevate your brand, optimize efficiency, and ensure distinctiveness in a competitive market.